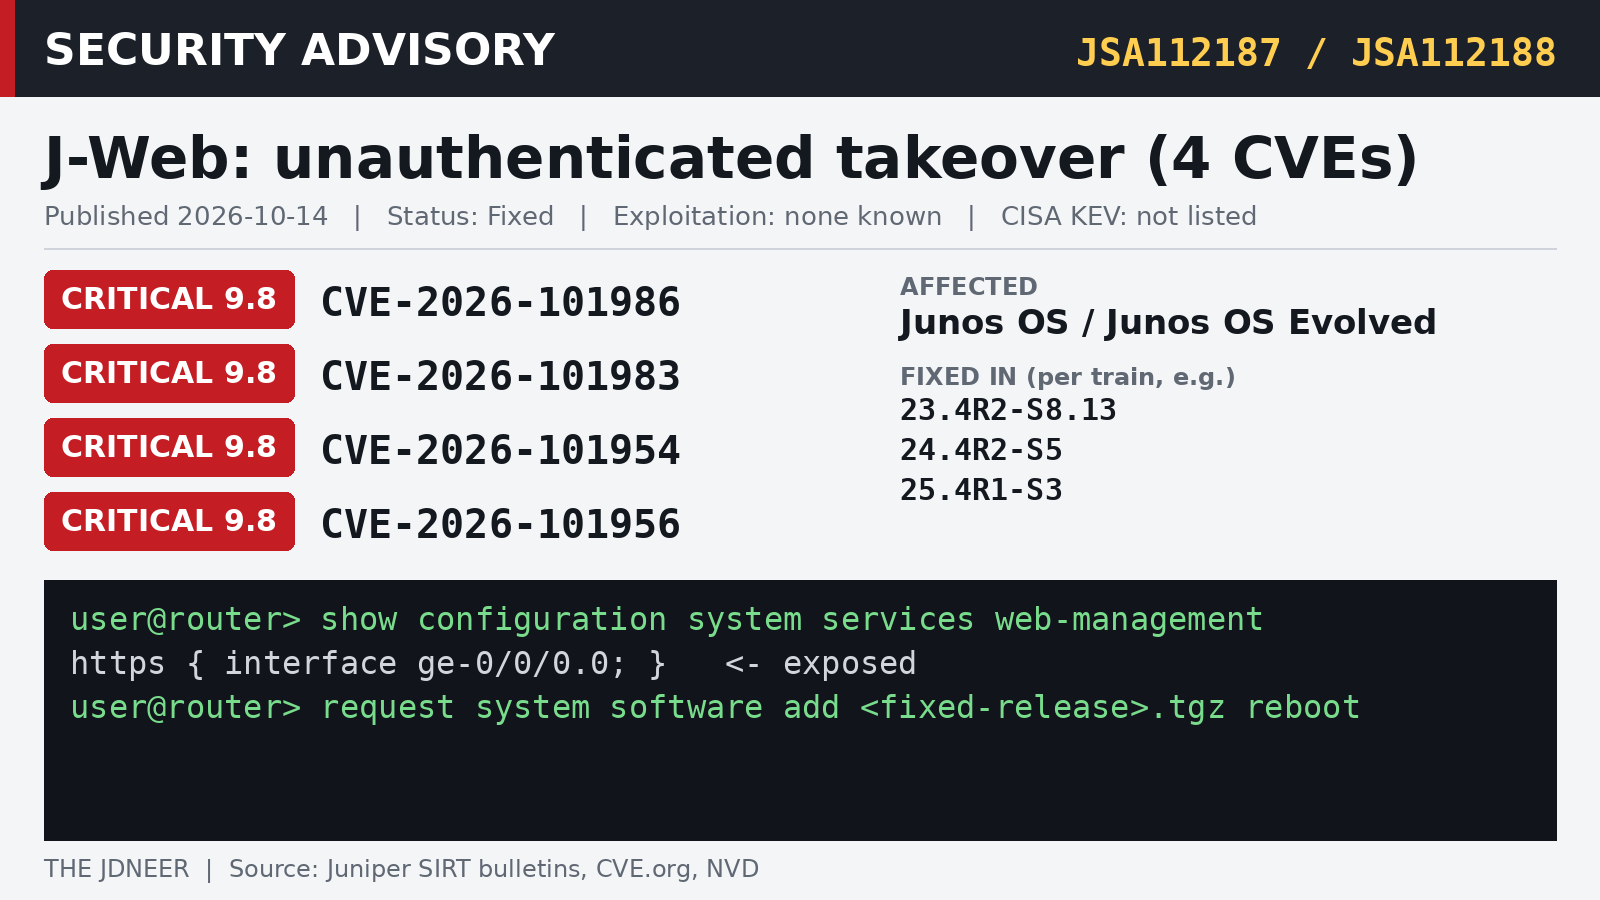
Four Critical J-Web Flaws Let Attackers Take Over Junos Devices Without Logging In
Juniper's October release fixes four CVSS 9.8 flaws in J-Web, the Junos web interface, that let unauthenticated attackers bypass login or run code as root. There are no workarounds, so patching and locking J-Web down to trusted hosts is the answer.